Waslوصل
Every event,
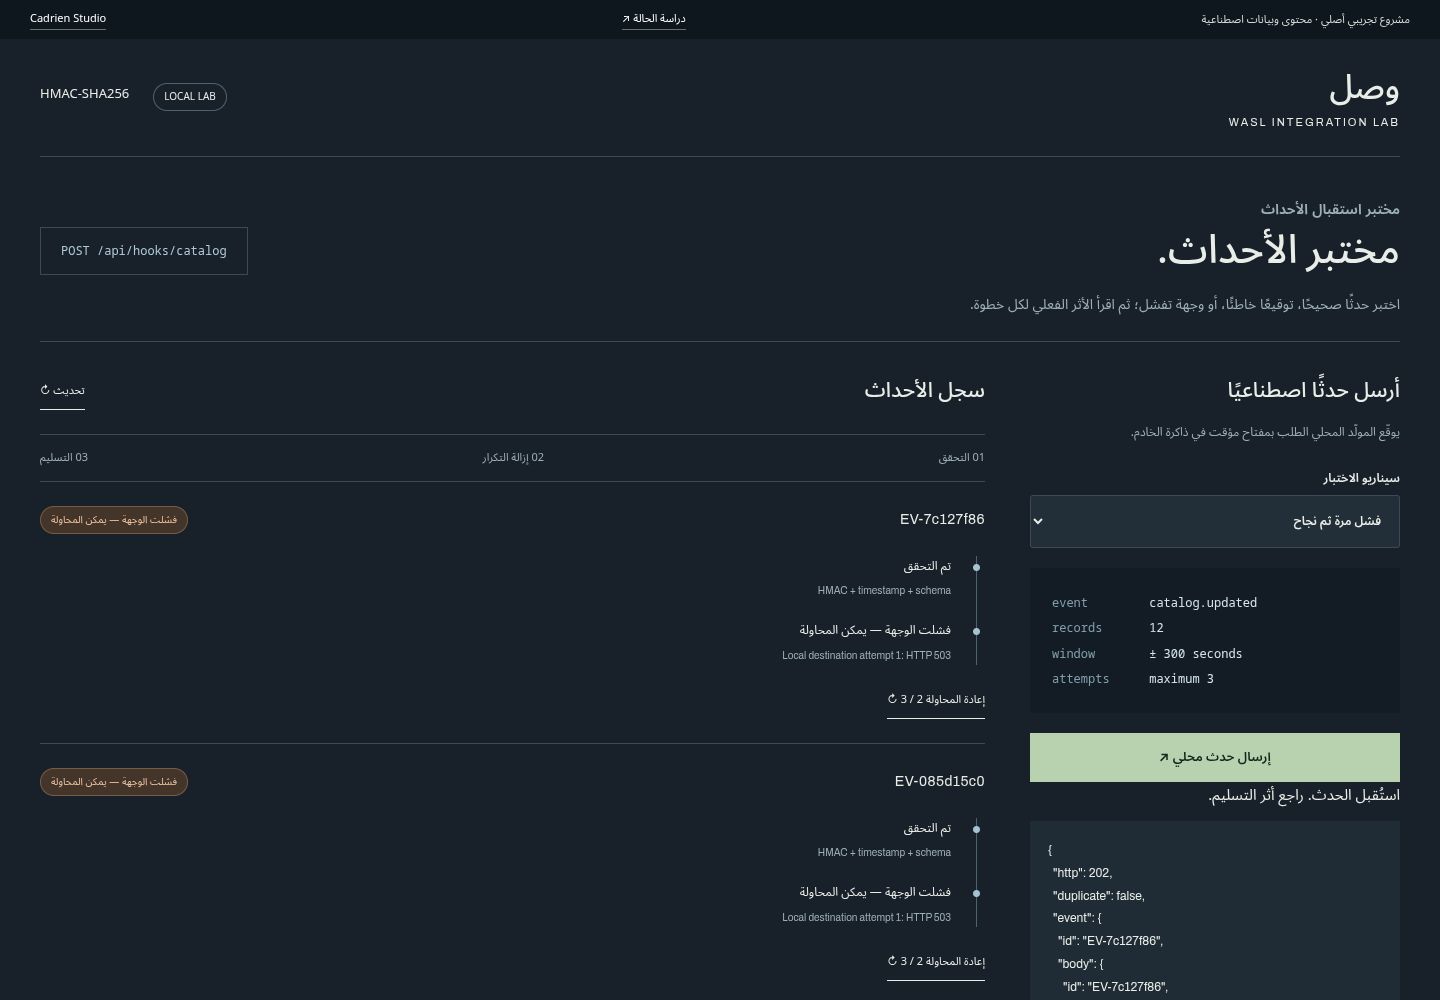
traceable.A local integration lab for signed webhooks: verify, de-duplicate, trace and retry — with a log that explains what happened.
The brief
An event can arrive twice, carry a bad signature or meet a failing destination. An integration needs defined behaviour for each case, and a record that explains what happened.
The approach
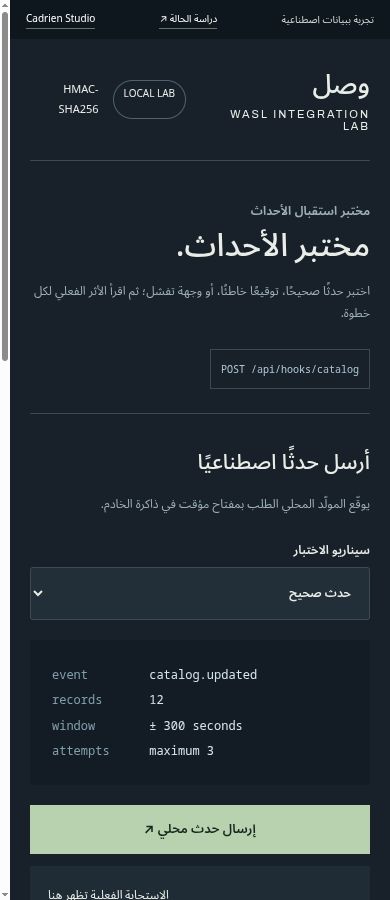
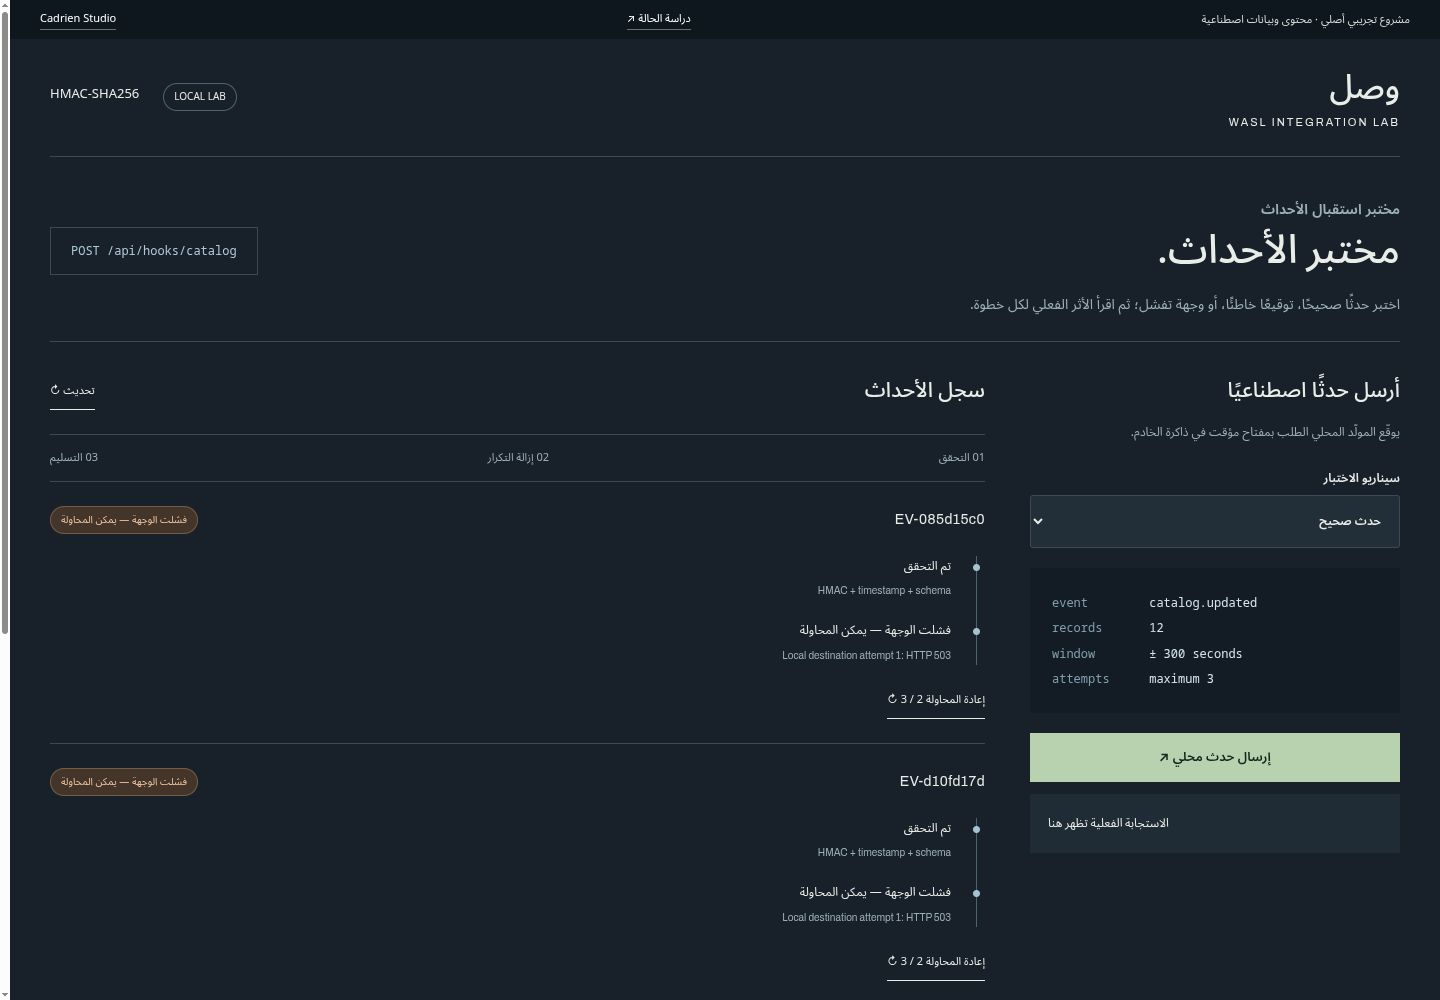
Wasl signs the raw request body with HMAC-SHA256 and checks a ±300-second timestamp window, the payload schema and an idempotency key. A local destination fails on purpose so that bounded retries can be exercised and traced.
What you can verify
- Send a valid, duplicated or wrongly signed synthetic event.
- Inspect the actual receive result and the processing trace.
- Retry a failed delivery until it succeeds or reaches the three-attempt limit.
- Duplicates are recognised by their idempotency key instead of being processed twice.
- API tests cover signature, timestamp, schema, duplicate and retry cases.
Implementation & handoff
A documented endpoint, a synthetic event sender, signature and timestamp verification, an attempt log and failure-case tests. Runs on your machine with Node.js 24.
Honest context
Destination outcomes are simulated locally; no external accounts or messages. The signing key is temporary and held in server memory. This is not a security audit or production middleware, and retries are manual and bounded inside the lab.